Cyber One Solutions logo.
Get Support

Latest Insights & Advisories

Cyber One Solutions Intelligence Desk

Decisions Get Easier When the Signal Is Clear.

Timely operational advisories, original security and compliance analysis, and practical technology guidance written for business leaders, not technical audiences.

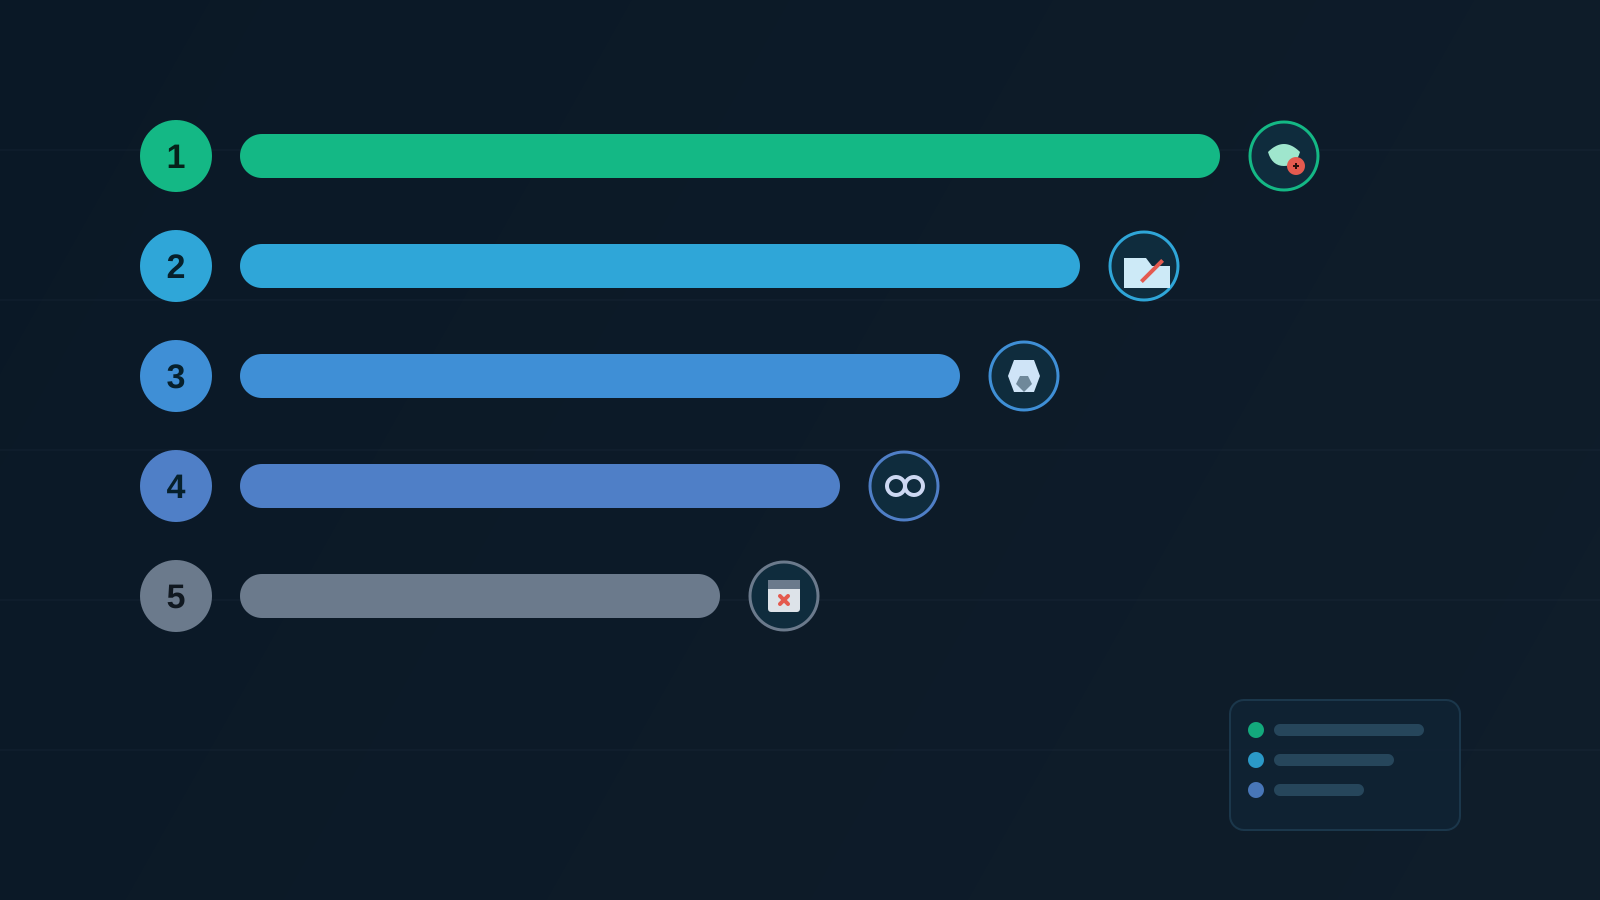
Five ranked priority bars of decreasing length, each tagged with an icon for a different flagged system: a spoofed-identity badge, a flagged file folder, a firewall/gateway shape, a tunnel connector, and a server with an expired calendar, representing this week's five ranked security and compliance developments.
Security & Compliance BriefSecurity Advisory

This Week's Top 5: A BeyondTrust Zero-Day by a Suspected Nation-State Actor, Five More Exploited Flaws, and the End of Windows Server 2012 Patching

CISA added nine actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog this week, including a BeyondTrust Remote Support zero-day that BeyondTrust and Google's Mandiant say a suspected nation-state actor used for nearly seven weeks before disclosure. Extended Security Updates for Windows Server 2012 and 2012 R2 also ended for good on October 13. Here are the five verified developments for small and mid-size businesses this week, ranked by relevance, exploitation evidence, and urgency.

October 18, 2026 10 min read
Read the Article
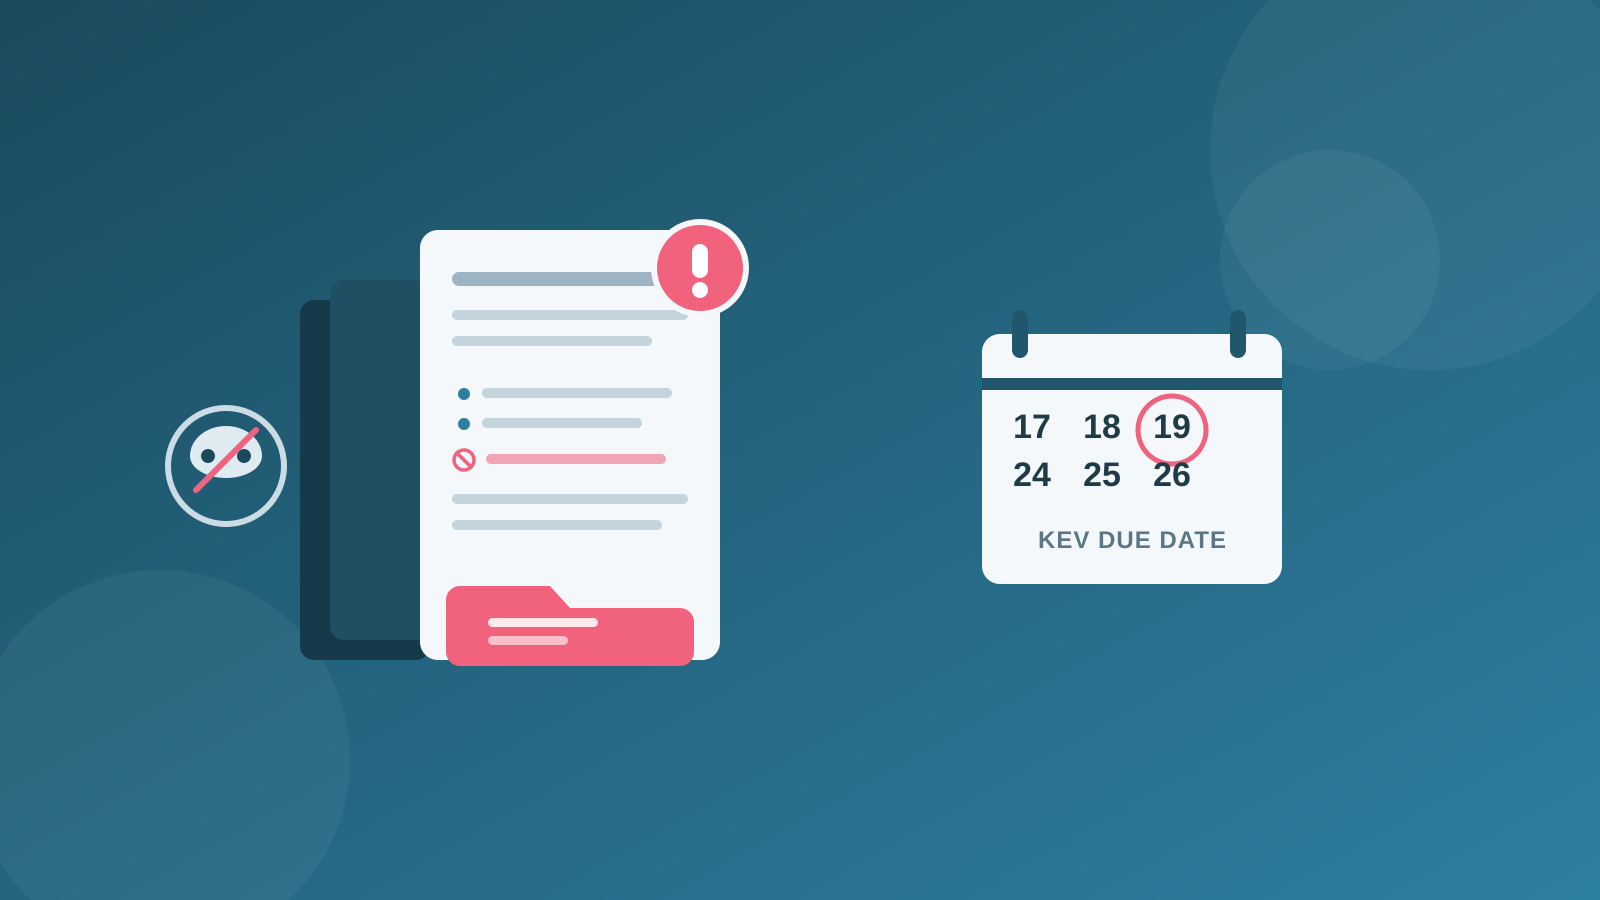
Illustration of a masked identity icon beside a remote-support appliance console with a flagged unvalidated message row, a red file-operations folder, and a critical alert badge, next to a calendar showing the 19th circled, representing a critical origin-validation flaw in self-hosted remote-support software with an October 19 CISA KEV due date.
News & AdvisoriesSecurity Advisory

CISA Adds Critical BeyondTrust Remote Support Flaw to Its KEV Catalog; BeyondTrust and Mandiant Confirm Zero-Day Exploitation by Suspected Nation-State Actor

CISA added CVE-2026-102764 to its Known Exploited Vulnerabilities catalog on October 16, 2026, the day after BeyondTrust and Google's Mandiant disclosed that a suspected China-nexus espionage actor exploited the flaw as a zero-day against BeyondTrust's Remote Support appliance in late August 2026. Here is who is affected, what BeyondTrust and Mandiant recommend beyond patching, and what to check now.

October 17, 2026 9 min read
Read the Article
Illustration of stacked application server panels with an open folder exposing a document and a red alert badge, beside a calendar showing the 18th circled, representing a critical unauthenticated file-access flaw in self-hosted collaboration software with an October 18 patch deadline.
News & AdvisoriesSecurity Advisory

CISA Confirms Active Exploitation of Critical Atlassian Data Center File-Access Flaw, Due October 18

CISA added CVE-2026-21589, a critical unauthenticated file-access flaw in eight self-hosted Atlassian products, to its Known Exploited Vulnerabilities catalog on October 15, 2026, with an October 18 remediation date, ten days after Atlassian's own advisory said it could not confirm whether any self-hosted instances were affected. Here is who is actually affected, what Atlassian has fixed, and what to check now.

October 16, 2026 7 min read
Read the Article
Illustration of a mail gateway appliance with a red alert badge and a firewall appliance with an amber alert badge, beside a calendar showing the 17th circled, representing two exploited network security flaws with an October 17 patch deadline.
News & AdvisoriesSecurity Advisory

Patch Before October 17: Exploited Flaws in Palo Alto PAN-OS and Cisco Secure Email Gateway

CISA added two actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog on October 14, 2026, both with an October 17 remediation date: a critical, unauthenticated file-write flaw in Cisco Secure Email Gateway (CVE-2026-76519) and a code injection flaw in Palo Alto Networks PAN-OS firewalls and Panorama (CVE-2026-0322). Here is who is affected, what each vendor confirmed, and what to check this week.

October 15, 2026 7 min read
Read the Article
Illustration of a network appliance under a keyhole shield, a document losing its internet-origin tag, and a calendar with one day highlighted, representing two exploited flaws with a patch deadline.
News & AdvisoriesSecurity Advisory

Patch Before October 16: Exploited Flaws in Ivanti Connect Secure and Windows Shell

CISA added two actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog on October 13, 2026, both with an October 16 remediation date: an authentication bypass in Ivanti Connect Secure VPN appliances (CVE-2026-104935) and a Windows Shell flaw that lets crafted files slip past Mark of the Web protections (CVE-2026-96951). Here is who is affected, what attackers have done with the Ivanti flaw, and what to check this week.

October 15, 2026 7 min read
Read the Article
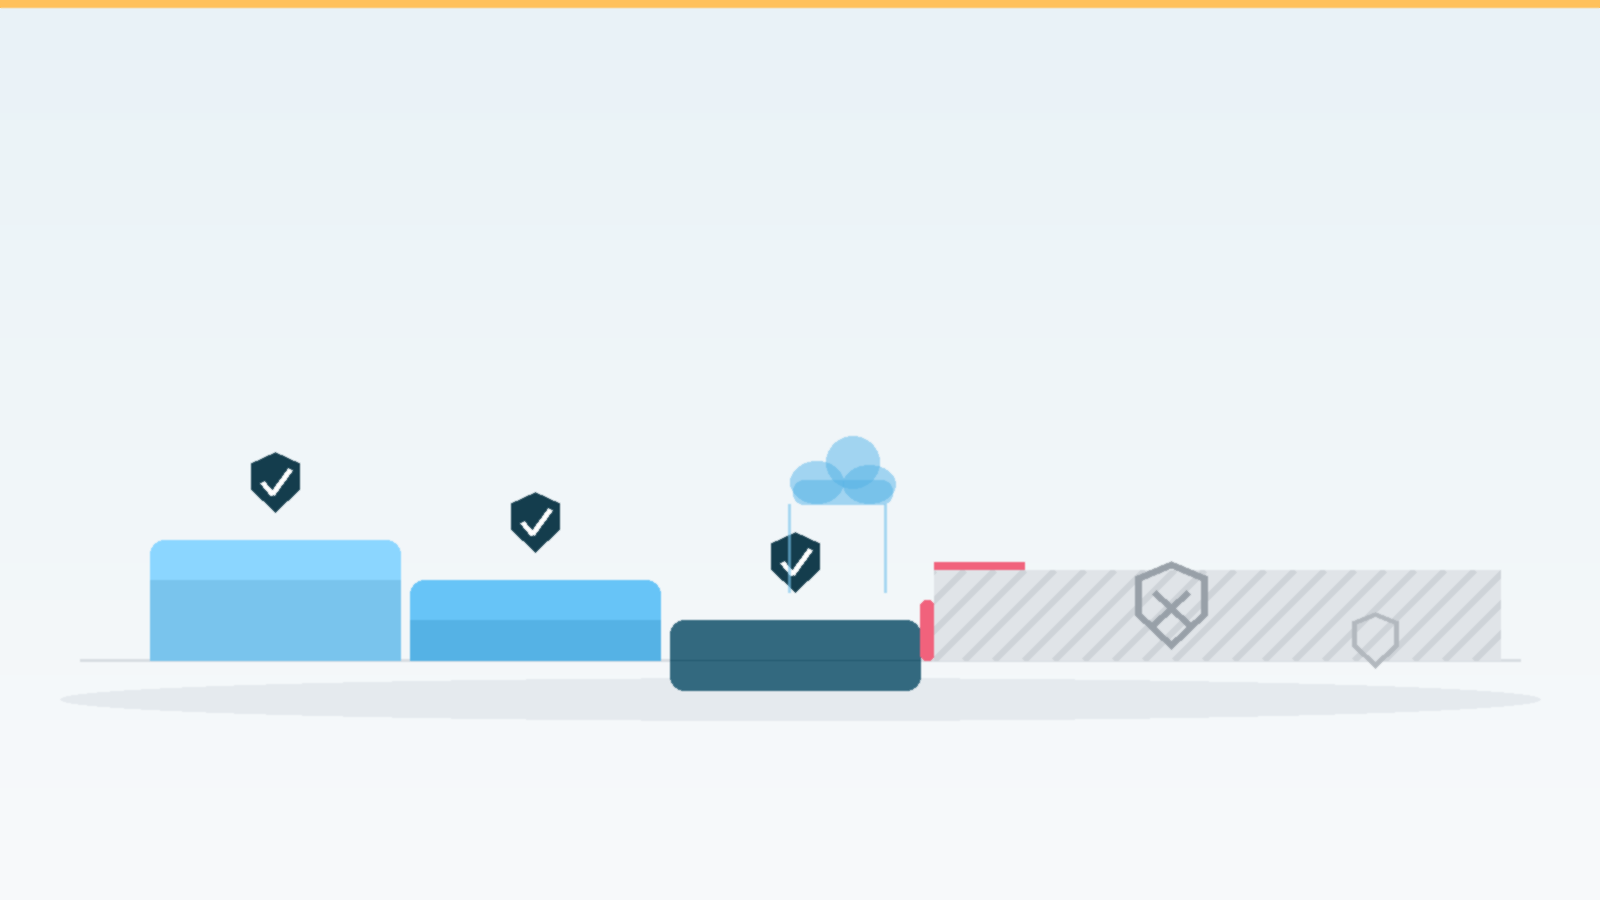
Illustration of three stepped platforms representing three years of Extended Security Updates, each covered by a checkmarked shield, ending at a red cutoff line with an empty, hatched gap and hollow shield icons beyond it.
News & AdvisoriesTechnology

Windows Server 2012 and 2012 R2: Extended Security Updates Have Ended, With No Fourth Year

Extended Security Updates for Windows Server 2012 and 2012 R2 ended with Microsoft's October 13, 2026 security update, the final one the program provides, and no further year is listed anywhere. That includes the free coverage Microsoft offered to workloads hosted in Azure for the same three years; it ended on the same date, not three years from whenever a workload actually migrated. If your business still has one of these servers in production, confirm it now and start moving off it.

October 15, 2026 7 min read
Read the Article
An authentication session token intercepted between two systems.
Business Technology BlogCybersecurity

Apple's Automatic Password Fix: What It Means for Business Security

Apple has announced that Apple Intelligence will change weak and compromised passwords for you in a future iOS 27 update, navigating supported sites and updating credentials automatically. It is a real step forward for password hygiene, but it is a consumer convenience, not a managed business control. Here is how it works and what your company still needs to own.

Updated October 12, 2026 6 min read
Read the Article